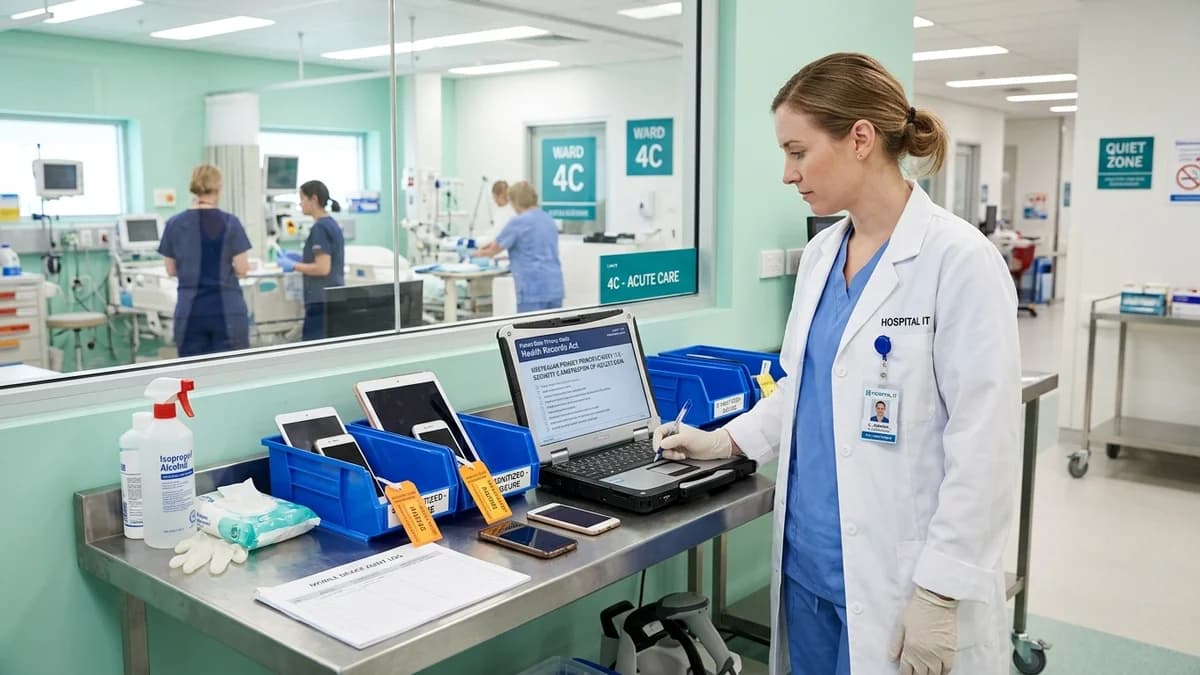
Executive Summary & Healthcare Governance
Healthcare providers, hospitals, medical centres, and dental clinics in NSW face strict statutory duties under Australian Privacy Principle 11.2 (APP 11.2) and the NSW Health Records and Information Privacy Act 2002 (HRIP Act) when retiring mobile hardware. Clinical smartphones and tablets retain cached pathology reports, patient clinical photographs, telehealth messaging transcripts, and patient identifiers. Phone Repair Centre delivers serialised NIST SP 800-88 Clear and Purge sanitisation with audit-ready certificates for RACGP and hospital accreditation.
The Hidden Patient Data Risk on Clinical Smartphones and Ward Tablets
Over the past five years, smartphones and tablets have become central to hospital workflows. Clinical ward staff, doctors, and allied health professionals use mobile devices for clinical messaging apps (such as Medtasker or WhatsApp groups), digital wound monitoring photography, e-script authorizations, and bedside patient consultations.
Even when mobile device management (MDM) software is deployed, local solid-state storage (eMMC and UFS) frequently retains unencrypted cached thumbnails, clinical image temporary files, and downloaded PDF pathology reports. If these devices are retired, donated, or traded in without forensically certified cryptographic sanitisation, the risk of a high-impact notifiable data breach is severe.
Statutory Privacy Obligations: APP 11.2 and NSW HRIP Act
Healthcare information is classified as sensitive data under Australian federal and state law:
| Regulatory Standard | Specific Statutory Obligation | Required Sanitisation Measure | Audit Documentation Required |
|---|---|---|---|
| Privacy Act 1988 (APP 11.2) | Entities must take reasonable steps to destroy or permanently de-identify personal information that is no longer needed. | NIST SP 800-88 Clear or Purge cryptographic erasure of all addressable storage sectors. | Serialised Certificate of Data Sanitisation per device IMEI. |
| NSW Health Records Act 2002 | Health Privacy Principle 5 (HPP 5) requires health service providers to protect health records from unauthorized disclosure and ensure secure disposal. | Irreversible sanitisation preventing recovery by laboratory forensic recovery tools. | Custody receipt and permanent asset disposal log. |
| Notifiable Data Breaches (NDB) | Mandatory reporting to the OAIC and affected patients if lost hardware leads to likely serious harm. | Proof of cryptographic sanitisation prior to hardware change of custody. | Tamper-proof audit report with cryptographic verification hashes. |
Accreditation-Ready Disposal Certificates for Medical Practices
Medical practices undergoing Royal Australian College of General Practitioners (RACGP) Standards 5th Edition accreditation must demonstrate robust information security protocols, including documented hardware retirement procedures.
Phone Repair Centre provides clinical healthcare clients with comprehensive compliance documentation:
- Individual Certificate per IMEI: Each smartphone, iPad, or mobile computer receives an individual certificate stating make, model, serial number, IMEI, erasure standard (NIST SP 800-88), method (Cryptographic Purge), date, and executing technician signature.
- Tamper-Proof Verification: Each document includes a verifiable cryptographic hash and QR code validation link.
- Reconciliation Register: A consolidated spreadsheet for your practice manager or hospital IT director to directly integrate into your institutional fixed asset compliance register.
Healthcare Mobile Decommissioning Checklist
- Identify all shared ward smartphones, clinical consultation tablets, and telehealth devices.
- Coordinate remote un-enrollment with your hospital MDM portal (Intune, MobileIron, Workspace ONE).
- Transport hardware in tamper-evident sealed containers directly to our accredited St Marys engineering lab.
- Execute NIST SP 800-88 Clear or Purge sanitisation across 100% of internal flash memory sectors.
- Physically shear and destroy any device with defective flash memory silicon that cannot be verified clean.
- File serialised Certificates of Sanitisation in practice accreditation and compliance binders.
IT Asset Disposition (ITAD / ATID) for Handset & Mobile Device Fleets in Sydney
Phone Repair Centre operates Sydney's flagship micro-electronics and ITAD laboratory at 122 Queen St, St Marys NSW 2760 with 18+ years of experience in Sydney. We provide direct corporate handset fleet decommissioning, NIST SP 800-88 Rev. 2 & Rev. 1 cryptographic sanitisation, APP 11.2 compliance certification, Level 4 logic board revival, and direct wholesale buyback payouts across Australia.
✓ NIST SP 800-88 Rev. 2 & APP 11.2 Sanitisation
Cryptographic Clear and Purge erasure with serialized, tamper-proof PDF certificates per IMEI. Fully aligned with Australian Privacy Principle 11.2 (APP 11.2) and APRA CPS 234 obligations.
✓ Level 4 Board Revival & OCA Glass Moat
Cracked or non-booting corporate handsets (iPhone, Samsung Galaxy, iPad, Zebra, Honeywell, ATID) are revived on our microsoldering bench to recover working residual value rather than broker shredding fees.
✓ Direct Lab Economics & Corporate EFT
Zero intermediary broker commissions. Transparent asset valuation reports with direct corporate EFT settlement to the verified ABN entity name against a formal Recipient Created Tax Invoice (RCTI).
✓ Tracked Chain of Custody & AS/NZS 5377:2013
Tamper-evident courier collection across Greater Sydney and Australia-wide with immediate serial intake reconciliation, ABM/Intune/Knox MDM lock verification, and Scope 3 carbon reporting.
Frequently Asked Questions
Does remote MDM wipe satisfy our hospital's APP 11.2 obligations?
A remote wipe command sent via MDM provides basic logical clearing, but it offers no forensic verification or certificate of media sanitisation that satisfies external privacy auditors. Bench-certified sanitisation confirms that all solid-state wear-leveling memory blocks have been cryptographically purged.
What happens to clinical devices that cannot turn on?
Any smartphone or tablet with damaged power rails is inspected in our micro-soldering lab. If the storage cannot be accessed to execute a verified purge, the device undergoes physical shearing, mechanically shredding the motherboard and memory chips, accompanied by a Certificate of Physical Destruction.
Can funds from retired medical fleet buybacks be credited back to our hospital?
Yes. Residual buyback payments are transferred via corporate EFT directly to the hospital, practice, or medical trust bank account matching the registered ABN.